Thursday, February 25, 2016

OWASP Connector Newsletter - February 25, 2016

OWASP Global Connector
Communications

ZAP Tops Toolswatch 2015 Survey!

OWASP Outreach - Surf to Snow in January

OWASP in the News

OWASP Podcasts

projects

New Project Releases

ZAP User Survey

Conference

Global AppSec Events

Local and Regional Events

Partner and Promotional Events

chapters

New OWASP Chapters

Chapter Restarts

Chapter Transitions

New Student Chapters


Chapter Activities

membership

New Contributing Corporate Members

Renewing Premier Corporate Members

Renewing Contributing Corporate Members

Social Media

OWASP Foundation Social Media


Communications

ZAP Tops Toolswatch 2015 Survey!

The Toolswatch 2015 Surveyresults are in:

ZAP is #1
OWTF is #10

The OWASP Zed Attack Proxy (ZAP) is an easy to use integrated penetration testing tool for finding vulnerabilities in web applications. It is designed to be used by people with a wide range of security experience and as such is ideal for developers and functional testers who are new to penetration testing. ZAP provides automated scanners as well as a set of tools that allow you to find security vulnerabilities manually.
OWASP OWTF is a project focused on penetration testing efficiency and alignment of security tests to security standards like: The OWASP Testing Guide (v3 and v4), the OWASP Top 10, PTES and NIST.

Download these tools at:
ZAP: https://www.owasp.org/index.php/ZAP
OWTF: https://www.owasp.org/index.php/OWASP_OWTF

Thank you to everyone who voted for OWASP tools! And congratulations to our ZAP and OWFT project teams

Surf to Snow in January!

#2 of our 2016 Strategic Goals is to become more involved in the Developer community. We are pleased to report tremendous turnout for our recent outreach events, Codemash in chilly Ohio and AppSec California in sunny Santa Monica.

CodeMash is a unique event that seeks to educate developers on current practices, methodologies, and technology trends in a variety of platforms and development languages such as Java, .NET, Ruby, Python and PHP.

A breakdown of this tremendous event: 
  • 2500 attendees
  • 1000 kids
  • 202 speakers
  • 84 staff
  • 280 sessions
    Sessions included 40 hours of security content, with 2 days of training by Jim Manico and Bill Sempf.

    OWASP Foundation participated as a Gold level sponsor. Bill Sempf, the project leader of the OWASP .NET Project and chapter leader for OWASP Columbus, served on the Session Committee helping to review over 1000 submissions. We have been proud to partner with Codemash over the past two years and are seeking similar opportunities worldwide.


    AppSec California is a one of a kind experience for information security professionals, developers, and QA and testing professionals, as they gather at the beach from around the world to learn and share knowledge and experiences about secure systems and secure development methodologies. The third annual event taking place last month fulfilled all expectations bridging the local application security and developer communities for a beautiful weekend on the California coast.


    Tell Us About Your Favorite Developer Events!


    We are looking for developer events to attend. Please Rate the top Developer Conferences where you would like to see OWASP participate. The survey will be open until EOD Feb, 29, 2016.

    Be sure to register for our upcoming events, such as Blackhat Asia 2016 on March 31 - April 1, 2016 at Marina Bay Sands, Singapore and invite your colleagues.


    OWASP in the NEWS!

    Match.com Learns that Encryption Alone Isn't Enough - ComputerWorld 2/19/2016

    Severe Glibc Flaw Puts Every Linux Machine in Danger - CIO Today 2/17/2016


    OWASP In Depth: An Interveiw with Jim Manico - SysCon Media 2/9/2016


    OWASP Podcasts

    OWASP Projects and activities are often the subject of webcasts and podcasts. Sit back and relax as you watch and listen to these recent episodes.

    OWASP Top 10 Proactive Controls Project with Jim Manico and Katy Anton


    The OWASP WebGoat Project, version 7.0, with Bruce Mayhew


    What's in Store for the OWASP 24/7 Podcast Series in 2016


    projects

    New Project Releases

    WebGoat V.7

    Webgoat v.7 released. Listen to our podcast as Bruce Mayhew explains the new version. The WebGoat Project started 10 years ago and has had over 1,000,000 downloads. Version 7.0 is being released this week. Matt Miller caught with Bruce Mayhew, project lead, to talk about the history of the project, what has been updated in version 7, and what he foresees as the future of this project. Project Page: http://www.owasp.org/index.php/CategorY:OWASP_WebGoat_Project.

    OWASP ZSC Project

    OWASP ZSC is an open source software in python language which lets you generate customized shellcodes and convert scripts to an obfuscated script. Shellcodes are small codes in assembly which could be use as the payload in software exploiting. Other usages are in malwares, bypassing anti viruses, obfuscated codes and etc. Obfuscate codes can be use for bypassing antiviruses, code protections, same stuff, etc. This software can be run on Windows/Linux/OSX under python.

    Why use OWASP ZSC?
    According to other shellcode generators such as metasploit tools and etc, OWASP ZSC using new encodes and methods which antiviruses won't detect. OWASP ZSC encoders are able to generate shellcodes with random encodes that lets you to get thousands of new dynamic shellcodes with the same job in just a second, it means you will not get a same code if you use random encodes with same commands, and that makes OWASP ZSC one of the bests! otherwise it's going to generate shellcodes for other operation systems in the next versions. It's the same story for the code obfuscation.


    Learn more at: https://www.owasp.org/index.php/OWASP_ZSC_Tool_Project.

    ESAPI

    ESAPI project co-leader, Kevin Wall announced his team has just tagged (and signed) a new ESAPI release. The tag name is esapi-2.1.0.1. There are 36 GitHub issues that were closed. You can find full details at: https://github.com/ESAPI/esapi-java-legacy/blob/master/documentation/esapi4java-core-2.1.0.1-release-notes.txt. Note that there are also some important changes made to the GitHub repo itself. Specifically, we have chosen to adopt a git workflow based on this blog: http://nvie.com/posts/a-successful-git-branching-model/, where all the new development work will be done on the 'develop' branch and the 'master' branch will henceforth reflect the latest official ESAPI release.

    ZAP User Survey

    Please help us to make @owasp ZAP even better for you by answering the ZAP User Questionnaire.

    Conference

    Global AppSec Events

    AppSec Europe 2016, 30 June - 1 July, 2016, Rome, Italy. Call for Lightning Trainings closes April 30. Call for Activities closes April 30.

    AppSec USA 2016, 11 October - 14 October 2016, Washington, DC

    Regional and Local Events

    Latam Tour 2016, April 7, 2016 - April 22, 2016, Latin America

    AppSec ASIA 2016, May 19, 2016 - May 22, 2016, Wuhan, China

    Partner and Promotional Events

    ONE2ONE SUMMIT, February 27 - February, 29, 2016, Parc 55 San Francisco, CA

    CISO Middle East Summit & Roundtable, February 29 - March 3, 2016, Habtoor Grand Hotel Dubai, The UAE. OWASP members save 20% by registering with your OWASP email address and discount code: OWASP2016

    Blackhat Asia 2016: March 31 - April 1, 2016, Marina Bay Sands Singapore, OWASP members receive a $200/USD discount on Briefings with discount code: OWBR0316

    Connected Security Expo, April 6 - April 8, 2016, Sands Expo Las Vegas, NV

    QuBit Conference, April 12 - April 14, 2016, Grandior Hotel Prague. OWASP members can save 10% by using their OWASP email address and discount code: OWASP*2016

    13th Annual CISO Europe Summit & Roundtable 2016, May 10 - May 13, 2016, Copenhagen Marriott, Denmark. OWASP members save 20% by registering with your OWASP email address and discount code: OWASP2016

    ONE2ONE SUMMIT, May 23 - May 25, 2016, Hotel Monteleone, New Orleans, LA

    Hack in the Box: May 26-27, 2016, Amsterdam, The Netherlands

    SC Congress Toronto: June 1, 2016 - June 2, 2016, Metro Convention Center Toronto, CN. Register today for an exclusive OWASP Member discount of $125. Full Conference pass sells for $350 Use the discount code - OWASPMEM

    Techno Security & Forensics Investigations Conference / Mobile Forensics World: June 5 - June 8, 2016, Myrtle Beach, SC, OWASP Members save 30% by using your @owasp email address and discount code: OWASP16

    ICCS 2016: July 25 - July 28, 2016, Fordham University at Lincoln Center, New York, NY

    Black Hat USA 2016: July 30 - August 4, 2016, Las Vegas, NV

    BSides Las Vegas: August 2 - August 3, 2016, Las Vegas, NV

    ONE2ONE SUMMIT: September 14 - September 16, 2016, Boca Beach Club, Boca Raton, FL

    (ISC)2 Security Congress EMEA 2016: October 18-19, 2016, Croke Park Stadium Dublin, Ireland


    Ads are not endorsements and reflect the messages of the advertiser only.They represent co-marketing arrangements
    with other organizations in support of the OWASP Community.   CLICK HERE for more information on advertising.
    ICCS 2016, July 25-28, 2016, Fordham University, New York, NY, USA Black Hat Asia 2016, March 29-April 1, 2015, Marina Bay Sands, Singapore
    CISO Middle East, 1-3 March 2016, Habtoor Grand Hotel, Dubai, UAE


    chapters

    New Chapters

    Chapter Restarts

    Transitions


    New Student Chapter

    Learn more about our Student Chapters and Academic Supporter programs.

    Notable Chapter Activity

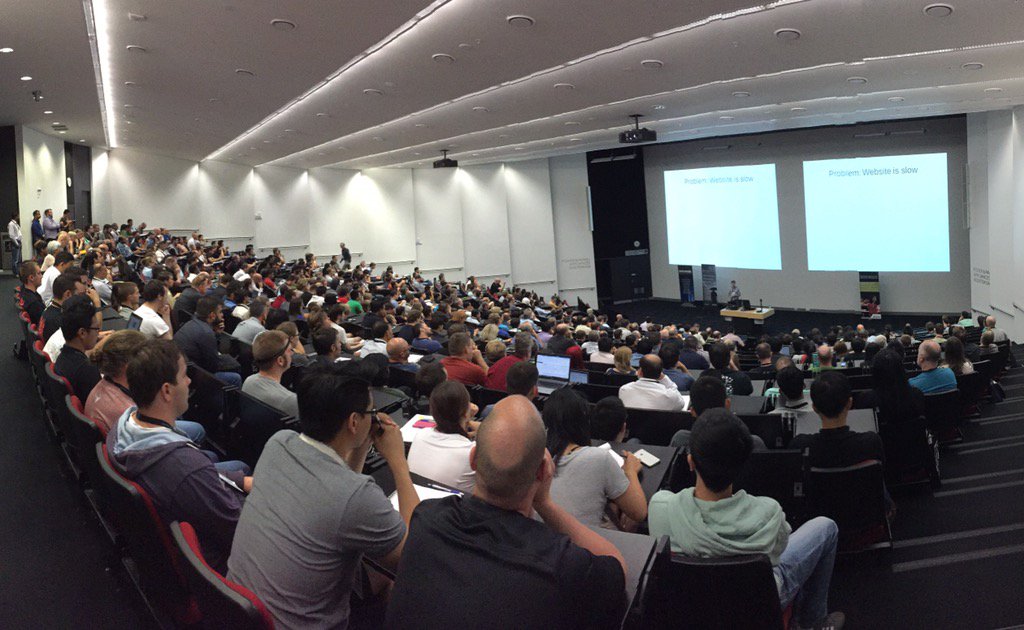
    OWASP New Zealand and the University of Aukland presented its seventh annual OWASP New Zealand Day on February 4. The OWASP New Zealand Day conference is a free, one-day event dedicated to application security, with an emphasis on secure architecture and development techniques to help Kiwi developers build more secure applications. The conference was preceded by a training event on February 3. Slide decks are posted to the 2016 OWASP New Zealand Day website.

    Who attended?

    • Web Developers: The morning sessions introduced attendees to application security. Afternoon sessions took a deeper dive into technical topics, building on the morning sessions.
    • Management: After an introduction to web application security, one of the afternoon streams focused on informational and defensive topics.
    • Security Professionals and Enthusiasts: Technical sessions later in the day showcased new and interesting attack and defense topics.


    A Cozy Evening at Snow FROC 2016


    Snow FROC 2016, took place this past week on February 18 in Denver, Colorado. The OWASP Colorado chapters hosted 200 developers, business owners, and security professionals for a day of presentations, training, and bonding. Jeremiah Grossman, Founder of WhiteHat Security, gave the keynote address, followed by a 2-track session and a parallel hands-on course.


    Lunch and Learn with OWASP NYC/NJ


    The OWASP NYC chapter has begun a series of virtual lunch and learn sessions about projects. The first call on February 23 featured the OWASP Benchmark project with Dave Wichers. Next month they will feature ASVS with Jim Manico. Full details for the 2016 program is available online at: http://www.meetup.com/metrocsc/. Raising appsec visibility one meeting at a time locally and globally, join us!

    Share Your Stories!

    We at the OWASP Global Foundation are looking forward to hearing about more such events in future. Share your chapter's successes! Submit your stories to support@owasp.org.

    OWASP Membership is a great way to contribute to our local chapters and projects. A portion of your membership can be allocated to teh chapter and/or project of your choice. Please show your support for OWASP Projects and Chapters by becoming an Individual or Corporate member today!


    Membership

    New Contributing Corporate Members

    • Onward Security Corporation

    Renewed Corporate Members (Premier Level)

    • Adobe
    • Contrast Security

    Renewed Corporate Members (Contributor Level)

    • Aspect Security
    • CA Technology
    • NetSPI
    • Oneconsult AG
    • WhiteHat Security
    Your name here? Find out how by visiting our Corporate Supporters information page. Thanks to all of our Premier and Contributing Corporate Members for your support in 2015!


    Social Media

    OWASP Social Media Site

    Labels: , ,

    Monday, February 15, 2016

    February 2016 Community News Flash


    February 2016 Community News Flash
    In this Issue:
    • FUNDING: Let's Talk About Funding and Plan for 2016!
    • PROJECTS: Announcing GSoC 2016, New Releases from OWASP ZSC, ESAPI, WebGoat 7, and a ZAP User Survey
    • CHAPTERS: New Chapters, Leader Transitions, Meeting Ideas for 2016
    • EVENTS: AppSec Europe and Other Upcoming Local and Regional Events
    • RESOURCES: List of Resources in this Issue

    FUNDING: Let's Talk About Funding and Plan for 2016!
    Get ready to share the OWASP vision and spread application security awareness. This January the OWASP Board released $33,000 to 65 Chapters! This is an incredible opportunity for formerly underfunded chapters to plan for the coming year.

    Join Community Manager Noreen Whysel and Projects Coordinator Claudia Aviles-Casanovas in an online discussion of Funding Ideas for 2016. We will be dialing in to GotoMeeting on February 12 and February 16. The call will be recorded if you are unable to attend. There will be two calls.

    Fri, Feb 12, 2016 12:00 PM - 1:00 PM EST
    Tue, Feb 16, 2016 8:00 AM - 9:00 AM EST

    Call details:

    PROJECTS: Announcing GSoC 2016, New Releases from OWASP ZSC, ESAPI, WebGoat 7, and a ZAP User Survey

    Got an Idea for Google Summer of Code 2016?

    The time of the year has come to propose ideas for GSoC 2016.

    We haven't been selected yet, but we need to populate this list of ideas as part of the organization application process.

    We have created a list here:

    We have removed last year's ideas and only left some as "example ideas". Please add more ideas to this list as you wish. You should put your ideas down before the application deadline, ie before February 19th. You will be able to add more idea after the deadline but we would like to present to Google as many ideas as possible.

    OWASP ZSC

    We are preparing to start developing a powerful obfuscation tool OWASP ZSC and looking for some volunteers to contribute the tool project.

    OWASP ZSC Project
    OWASP ZSC is an open source software in python language which lets you generate customized shellcodes and convert scripts to an obfuscated script. This software can be run on Windows/Linux/OSX under python.

    Usage of shellcodes
    Shellcodes are small codes in assembly which could be use as the payload in software exploiting. Other usages are in malwares, bypassing anti viruses, obfuscated codes and etc.

    Usage of Obfuscate Codes
    Can be use for bypassing antiviruses, code protections, same stuff etc…

    Why use OWASP ZSC ?
    According to other shellcode generators such as metasploit tools and etc, OWASP ZSC using new encodes and methods which antiviruses won't detect. OWASP ZSC encoders are able to generate shellcodes with random encodes that lets you to get thousands of new dynamic shellcodes with the same job in just a second, it means you will not get a same code if you use random encodes with same commands, and that makes OWASP ZSC one of the bests! otherwise it's going to generate shellcodes for other operation systems in the next versions. It’s the same story for the code obfuscation.

    There are more details about how it works and user guides and also how to develop.
    And whole developer and users guide documents are available for download in gitbooks.

    Developers can add new features and if you don’t have idea but like to develop, you can find the issue which software needed to be fix/add/done HERE.

    After fix/add or develop something, please send your pull request and remember that your code must be compatible with python2 and python3.

    If you have any question you can open an issue or just mail us. Do not forget to register on our mailing list.

    If there is any questions, you can submit it in issues on github, mail us or contact the Project leaders directly.

    ali.razmjoo@owasp.org
    johanna.curiel@owasp.org
    owasp-zsc-tool-project@lists.owasp.org

    URLs:


    WebGoat v.7

    Webgoat v.7 released. Listen to our podcast as Bruce Mayhew explains the new version. The WebGoat Project started 10 years ago and has had over 1,000,000 downloads. Version 7.0 is being released this week. Matt Miller caught with Bruce Mayhew, project lead, to talk about the history of the project, what has been updated in version 7, and what he foresees as the future of this project. Project Page: http://www.owasp.org/index.php/CategorY:OWASP_WebGoat_Project

    New ESAPI Release

    ESAPI project co-leader, Kevin Wall announced his team has just tagged (and signed) a new ESAPI release. The tag name is esapi-2.1.0.1. There are 36 GitHub issues that were closed. You can find full details at: https://github.com/ESAPI/esapi-java-legacy/blob/master/documentation/esapi4java-core-2.1.0.1-release-notes.txt.
    Note that there are also some important changes made to the GitHub repo itself. Specifically, we have chosen to adopt a git workflow based on this blog: http://nvie.com/posts/a-successful-git-branching-model/, where all the new development work will be done on the 'develop' branch and the 'master' branch will henceforth reflect the latest official ESAPI release.

    To accommodate this,
    • The 'develop' branch has now been made the DEFAULT branch.
    • The 'master' branch has now been made a PROTECTED branch.
    Chris Schmidt will be uploading this to Maven sometime later this day, probably once he's through with his day job. Lastly, a special shout-out to Matt Seil and Jeremiah Stacey for their help with Git and some nasty JUnit concurrency issues.

    ZAP User Survey

    Please help us to make @owasp ZAP even better for you by answering the ZAP User Questionnaire: https://docs.google.com/forms/d/1-k-vcj_sSxlil6XLxCFade-m-IQVeE2h9gduA-2ZPPA/viewform

    A Call for Comments on the OWASP Projects Handbook update is now open. We invite project participants to visit the OWASP Projects Handbook draft on Google Docs and enter comments. You can also download a PDF version from the OWASP Projects wiki page and forward comments to Claudia Aviles-Casanovas at claudia.aviles-casanovas@owasp.org.

    OWASP 24/7 PodCasts


    We now have 72 podcasts for your listening pleasure. Knock yourself out!

    Created by Mark Miller, OWASP 24/7 Podcasts offer a great forum for getting an update on projects. Listen to interviews with project leaders at https://soundcloud.com/owasp-podcast.

    CHAPTERS: New Chapters, Leader Transitions, Meeting Ideas for 2016

    New Chapters

    Restarted Chapters
    Leader Transitions
    • Cluj, Romania: Lucian Suta and Cristian Serban, new leaders. Much appreciation owed to Lucian Corlan who founded the chapter last year and developed wonderful public programs on application security with local government.
      https://www.owasp.org/index.php/Cluj
       
    • Kolkata, India: Jitendra Adhikari (Jitendra.Adhikari@owasp.org) and Tanmoy Khanra (Tanmoy.Khanra@owasp.org) join the leadership team with Krishnendu Paul. Dibyendu Sikdar is stepping down. Many thanks to Dibyendu for your service to OWASP Kolkata.
      https://www.owasp.org/index.php/Kolkata
    There are many leader openings for chapters that have gone inactive, particularly in the Middle East and Africa. Go to the Volunteer page for a listing of open positions: http://owasp.force.com/volunteers/GW_Volunteers__VolunteersJobListing

    New Student Chapters
    Learn more about our Student Chapters and Academic Supporter programs.

    Restarting an Inactive Chapter

    If you are interested in starting or helping to restart a chapter that has gone inactive, please review the listings at the Volunteer Opportunities page of the wiki. If you are a current chapter leader and are having difficulty finding space, volunteers or funding to host a meeting, let me know. I can direct you to resources and funding to help you.

    Also keep in mind you can view your Chapter's budget and available funds at the Donation Scoreboard:

    EVENTS: Upcoming AppSec Events
    The European OWASP Conference is going to be one of the best ever.
    Come to hear and share ideas with the experts! 
    27 June - 1 July 2016

    Read the latest news on the next OWASP AppSecEU on the conference site: http://2016.appsec.eu/

    Important keynote speakers will be present at the Marriott Park Hotel in Rome, Italy.

    Our special guest will be Charlie Miller, who will present the keynote talk "Bugs ruin everything". In his speech, Miller will discuss some popular methods for finding vulnerabilities and why it is so difficult to spot them.

    Charlie Miller is a senior security engineer at Uber ATC, a hacker, and a gentleman. Back when he still had time to research, he was the first with a public remote exploit for both the iPhone and the G1 Android phone. He is a four-time winner of the CanSecWest Pwn2Own competition. He has authored three information security books and holds a PhD from the University of Notre Dame. He has hacked browsers, phones, cars, and batteries.

    The Open Web Application Security Project is an open-source project for application security. OWASP provides advice on the creation of secure Internet applications and testing guides.

    It boasts a strong global community with more than 45,000 participants, more than 55 corporate members and 20 academic supporters through 249 active local chapters in 6 continents and 97 countries.

    More than 800 people are expected at the event, with 3 days of training followed by the 2-day conference that includes:
    • Five parallel talks with focus on the OWASP core mission (Dev, Ops, Hack, CISO and Research);
    • Keynotes from industry leaders;
    • Exhibition spaces that offer innovative solutions for the needs of companies.
    Do not miss the opportunity to participate this important conference, mentioned in Tripwire as a TOP 11 SECURITY CONFERENCE IN 2016.

    More details on registration, program and speakers will be sent in a forthcoming communication.

    Global AppSec Events
    • AppSec Europe 2016, 30 June - 1 July, 2016, Rome, Italy
    • AppSec USA 2016, 11 October - 14 October 2016, Washington, DC
    Regional and Local Events
    Partner and Promotional Events
    • SC Congress London: February 10, 2016, ILEC Conference Centre London, UK. Register today for an exclusive OWASP Member discount of $125. Full Conference pass sells for $350 Use the discount code - OWASPMEM
    • ONE2ONE SUMMIT, February 27 - February, 29, 2016, Parc 55 San Francisco, CA
    • CISO Middle East Summit & Roundtable, February 29 - March 3, 2016, Habtoor Grand Hotel Dubai, The UAE. OWASP members save 20% by registering with your OWASP email address and discount code: OWASP2016
    • Blackhat Asia 2016: March 31 - April 1, 2016, Marina Bay Sands Singapore
    • Connected Security Expo, April 6 - April 8, 2016, Sans Expo Las Vegas, NV
    • QuBit Conference, April 12 - April 14, 2016, Grandior Hotel Prague. OWASP members can save 10% by using their OWASP email address and discount code: OWASP*2016
    • 13th Annual CISO Europe Summit & Roundtable 2016, May 10 - May 13, 2016, Copenhagen Marriott, Denmark. OWASP members save 20% by registering with your OWASP email address and discount code: OWASP2016
    • ONE2ONE SUMMIT, May 23 - May 25, 2016, Hotel Monteleone, New Orleans, LA. OWASP members receive a $200/USD discount on Briefings with discount code: OWBR0316
    • SC Congress Toronto: June 1, 2016 - June 2, 2016, Metro Convention Center Toronto, CN. Register today for an exclusive OWASP Member discount of $125. Full Conference pass sells for $350 Use the discount code - OWASPMEM


    Watch the AppSec Conference page for updated event listings. Be sure to enter your upcoming event into the OWASP Conference Management System so we can promote it and provide assistance.

    RESOURCES

    Project Inventory:
    https://www.owasp.org/index.php/OWASP_Project_Inventory
    https://www.owasp.org/index.php/Category:OWASP_Project


    Google Summer of Code 2016 Ideas:
    https://www.owasp.org/index.php/GSOC2016_Ideas


    OWASP ZSC Tool: 
    https://www.owasp.org/index.php/OWASP_ZSC_Tool_Project

    WebGoat v.7: 
    http://www.owasp.org/index.php/Category:OWASP_WebGoat_Project

    ESAPI Release
    https://github.com/ESAPI/esapi-java-legacy/blob/master/documentation/esapi4java-core-2.1.0.1-release-notes.txt


    ZAP User Questionnaire
    https://docs.google.com/forms/d/1-k-vcj_sSxlil6XLxCFade-m-IQVeE2h9gduA-2ZPPA/viewform


    Chapter Leader Handbook:
    https://www.owasp.org/index.php/Chapter_Leader_Handbook


    Funding Resources:
    https://www.owasp.org/index.php/Funding


    Donation Scoreboard - Current Chapter and Project Funding Allocations:
    https://docs.google.com/spreadsheets/u/2/d/11acTOmtmBGq6-5CIGsjlEByU8POSGqda0r23VNnhEGQ/pub?hl=en_US&hl=en_US&output=html


    OWASP Conference Management System:
    https://www.owasp.org/index.php/Owasp_Conference_Management_System


    CONTACT ME
    Feel free to contact me at any time if you have a question or suggestion. To create a trackable case, please use the contact us form at http://www.tfaforms.com/308703.

    Noreen Whysel
    Community Manager
    OWASP Foundation


    Community Manager Open Hours on Slack:
    Join the #AsktheCM channel Tuesdays from 10am-Noon EDT.
    https://owasp.slack.com/messages/askthecm/


    Labels: ,

    Wednesday, January 27, 2016

    OWASP Connector Newsletter - January 27, 2016

    January 27, 2016 | www.owasp.org | Contact Us | Brought to you by the OWASP Foundation
    Communications

    2016 OWASP Strategic Goals

    OWASP in the News

    OWASP Podcasts

    projects

    Project Review Team Members Announced

    OWASP Proactive Controls Top
    Ten V2 Release

    OWASP Security Knowledge Framework Project Release

    New Cornucopia Web Edition

    ZAP: XCOLD Information Leaks

    Transaction Authorization Cheat Sheet Update

    ZSC Tools Volunteers Needed

    Conference

    Global AppSec Events

    Local and Regional Events

    Partner and Promotional Events

    chapters

    New OWASP Chapters

    Chapter Restarts

    Chapter Transitions

    New Student Chapters

    Chapter Activities

    membership

    Corporate Members: Why Not
    You?

    Social Media

    OWASP Foundation Social Media


    Communications

    2016 OWASP Strategic Goals Announced

    The 2016 OWASP Strategic Goals are available to review. Five goals will guide our programs in the coming year:
    1. Education & Training
    2. Expand Outreach, specifically to the Developer Community
    3. Mature the OWASP Projects Platform
    4. Community & Chapter Support
    5. Enhance the OWASP Infrastructure
    Look for an update shortly on the OWASP Blog from the board for further details.

    OWASP in the NEWS!

    Security Innovation Making Splash OWASP AppSec California - BusinessWire 1/25/2016

    OWASP's Revamped Developer Guide will Help You Pass Pen Tests (Interview with Andrew Van der Stock on OWASP Application Security Verification Standard 3.0)- The Register 1/12/2016

    Security Brief - Protecting Against the OWASP Mobile Top 10 - App Developer Magazine 1/7/2016

    OWASP AppSec EU made list of the Top 11 Security Conferences in the world! - Tripwire 1/5/2016

    OWASP Podcasts

    OWASP Projects and activities are often the subject of webcasts and podcasts. Sit back and relax as you watch and listen to these recent episodes.

    What's in Store for the OWASP 24/7 Podcast Series in 2016

    projects

    Project Review a Team Members Announced

    We are happy to announce that we have formed a team of volunteers for the Project Review Committee to relaunch the Project review team and incentives for projects.

    • Timo Goosen
    • Christo Goosen
    • Enrico Branca
    • Johanna Curiel
    • Tom Brennan ==> As part of the Board members and now leading Projects
    We are redefining the goals of the Project Review Team (mostly known as the Project task force) but we want to create clear goals by redefining some of the original committee goals launched almost 2 years ago.

    Main changes to this committee goals will be:

    • Handling the process for starting new projects and reviewing submitted proposals
    • Guide new leaders to take that idea into a feasible and realizable project
    • Create webinars/meetings with regional leaders to promote guidelines
    • Create a Handbook & Guidelines for starting a new project and maintaining the project guidelines
    • Implement a portal for project reviews & reporting through Github which Enrico has already worked on Automation and monitoring of new projects and existing projects
    • Implement a fixed QA review for project graduation with professional testers as we did back in 2014 major reviews
    • Look for sponsors and create specific budget for the committees activities
    • Create incentives for projects as explained on this proposal: https://docs.google.com/document/d/1PvNeEWgoO1w51VhHLwqqSgo0mBh-RvmSFUKMTz4QrYg/edit#heading=h.lw77ixr6kxi

    If you want to be part of the team and would like to provide feedback. We are looking for:

    • Evaluators of new projects
    • Season Reviewers for quarterly major reviews
    • Help monitor the wiki pages and alerts
    Keep in mind you can always provide feedback anytime through: https://groups.google.com/a/owasp.org/forum/#!forum/owasp-project-reviews


    OWASP Proactive Controls Top Ten V2 Release

    We just released the OWASP Proactive Controls Top Ten v2. (Download PDF). Big thanks Jim Bird and Katy Anton for their dedication in making this release a reality. This document is a "developer centric" answer to the OWASP Top Ten. It's meant to be an awareness document to inform developers about the basics of building secure software. As a process, we made the document "world editable" and fielded literally hundreds of community change requests (many from anonymous sources) from to hopefully represent consensus in our community. 

    Thanks to everyone who helped make this happen. We hope it helps serve the cause in some way.


    OWASP Security Knowlege Framework Project Release

    A new release of the OWASP Security Knoledge Framework project is available! https://www.owasp.org/index.php/OWASP_Security_Knowledge_Framework
    https://www.securityknowledgeframework.org


    Cornucopia Web Edition Released

    OWASP Cornucopia project co-leader Darío De Filippis conceived, created and published a wiki version of "OWASP Cornucopia - Ecommerce Website Edition", the web application security training and threat modeling card game. The wiki deck, comprising 91 new pages, complements the existing print versions and provides a single place to easily browse around the suits and cards, jump to the relevant cross-references, and most importantly includes an extra technical note for each card. The technical notes supplement the card text, providing additional information on each threat and attack. It also aids game play by providing some clarification between cards which at first might seem similar.


    The project team welcomes any contributions to correct, extend, and improve the technical notes for each card. 

    The wiki deck can be found at:
    https://www.owasp.org/index.php/Cornucopia_-_Ecommerce_Website_Edition_-_Wiki_Deck


    The main project page, including FAQs, how to play video, presentation, and how to obtain the decks of cards is at https://www.owasp.org/index.php/OWASP_Cornucopia

    ZAP: XCOLD Information Leaks

    Have you heard about X-ChrOmeLogger-Data (XCOLD) Information leaks? No?? Then you better read the latest ZAP Newsletter!
    http://zaproxy.blogspot.co.uk/2016/01/zap-newsletter-2016-january.html


    Transaction Authorization Cheat Sheet Update

    An updated version of our Transaction Authorization Cheat Sheet available:
    https://www.owasp.org/index.php/Transaction_Authorization_Cheat_Sheet


    ZSC Tools Volunteers Needed

    The ZSC Tool project needs volunteers. For details, visit https://www.owasp.org/index.php/OWASP_ZSC_Tool_Project


    Conference

    Global AppSec Events

    OWASP AppSecEU

    The European OWASP Conference is going to be one of the best ever.
    Do not miss this opportunity!
    7 June - 1 July 2016


    Thanks to the impressive number of paper submissions received, the qualified organisations and people that submitted them and the important sponsors, this will be one of the best OWASP conferences ever. Do not miss the opportunity to hear and share ideas and knowledge with a wide number of experts!

    The next OWASP AppSecEU (http://2016.appsec.eu/) will take place at the Marriott Park Hotel in Rome, Italy.

    The Open Web Application Security Project is an open-source project for application security. OWASP provides advice on the creation of secure Internet applications and testing guides.

    It boasts a strong global community with more than 45,000 participants, more than 55 corporate members and 20 academic supporters through 249 active local chapters in 6 continents and 97 countries.

    More than 800 people are expected at the event, with 3 days of training followed by the 2-day conference that includes:
    • Five parallel talks with focus on the OWASP core mission (Dev, Ops, Hack, CISO and Research);
    • Keynotes from industry leaders;
    • Exhibition spaces that offer innovative solutions for the needs of companies.
    Do not miss the opportunity to participate as SPONSOR to this high level conference, mentioned in Tripwire as a TOP 11 SECURITY CONFERENCE IN 2016.

    More details on registration, program and speakers will be sent in a forthcoming communication.

    Please contact us with any questions or comments you may have at the following address:
    appseceu2016@owasp.org


    Other Global AppSec Events

    AppSecUSA 2016 will be held on 11-14 October 2016 in Washington DC. Mark your calendars!

    Regional and Local Events

    AppSec Cali 2016, Jan. 25, 2016 - Jan. 27, 2016, Santa Monica, CA

    New Zealand Day 2016, February 3, 2016 - February 4, 2016, Auckland, New Zealand

    Snow FROC 2016, February 18, 2016, Denver, CO

    Latam Tour 2016, April 7, 2016 - April 22, 2016, Latin America

    CyberSecurity 2016, May 16, 2016 - May 20, 2016, New York, NY, USA

    AppSec ASIA 2016, May 19, 2016 - May 22, 2016, Wuhan, China

    Partner and Promotional Events

    IoT Evolution Expo, January 25 - 28 , 2016 Ft. Lauderdale, FL - OWASP Members receive 25% off the list ticket cost by using discount code: OWASP

    SC Congress London, February 10, 2016 ILEC Conference Centre London, UK

    Blackhat Asia 2016, March 31 - April 1, 2016 Marina Bay Sands, Singapore. OWASP members receive a $200/USD discount on Briefings with discount code: OWBR0316

    SC Congress Toronto, June 1, 2016 - June 2, 2016 Metro Convention Center Toronto, CN


    Ads are not endorsements and reflect the messages of the advertiser only. They represent co-marketing arrangements
    with other organizations in support of the OWASP Community. CLICK HERE for more information on advertising.

    chapters

    New Chapters

    Chapters Restarts

    Transitions

    New Student Chapter

    • Amity University Rajasthan-Jaipur
      Contact: Harsh Bothra (hani22499@gmail.com), student leader
       
    • Information Technology Institute, Cairo, Egypt
      Faculty Advisor: Mrs. Lamia Mostafa, (lmostafa@mcit.gov.eg)
    Learn more about our Student Chapters and Academic Supporter programs.

    Notable Chapter Activity

    Funding Updates

    Some of our chapters and projects that ended the year with less than $500 will be seeing an increase in their funding allocations. It is our hope that these addition will help active chapters to jumpstart their activities for the new year without worry that they will not be able to afford to host a meeting. Chapters and projects with current activity and at least two leaders got an increase and we will soon announce a series of calls to discuss ideas for renewed activities.

    One of the best ways for our projects and chapters to raise funds is to recruit new, paid memberships and local sponsors. Individual memberships are a low $50 per year (pro rated in some countries) and corporate memberships are available at $5,000, $20,000 and $50,000, a portion of which can be allocated to a chapter and/or project. Local sponsorships are available in smaller amounts and can be allocated directly to a project or chapter, making a valuable contribution to their activities. Interested local sponsors can make a contribution via the "Donate" button on your favorite chapter or project's wiki page.

    Please show your support for OWASP Projects and Chapters by becoming an Individual or Corporate member today!

    We at the OWASP Global Foundation are looking forward to hearing about more such events in future.

    Share your chapter's successes! Submit Your Stories


    Membership

    New Contributing Corporate Members

    Thanks to all of our Premier and Contributing Corporate Members for your support in 2015!

    Social Media

    OWASP Social Media Site

    Labels: ,